
6.7 Syslog
Administration → Settings → Syslog. Forwards Ada’s logs to one or more syslog servers (SIEM). Forwarding is independent of the Alerts page: every audit record is forwarded to each matching server, whether or not an alert category is on.
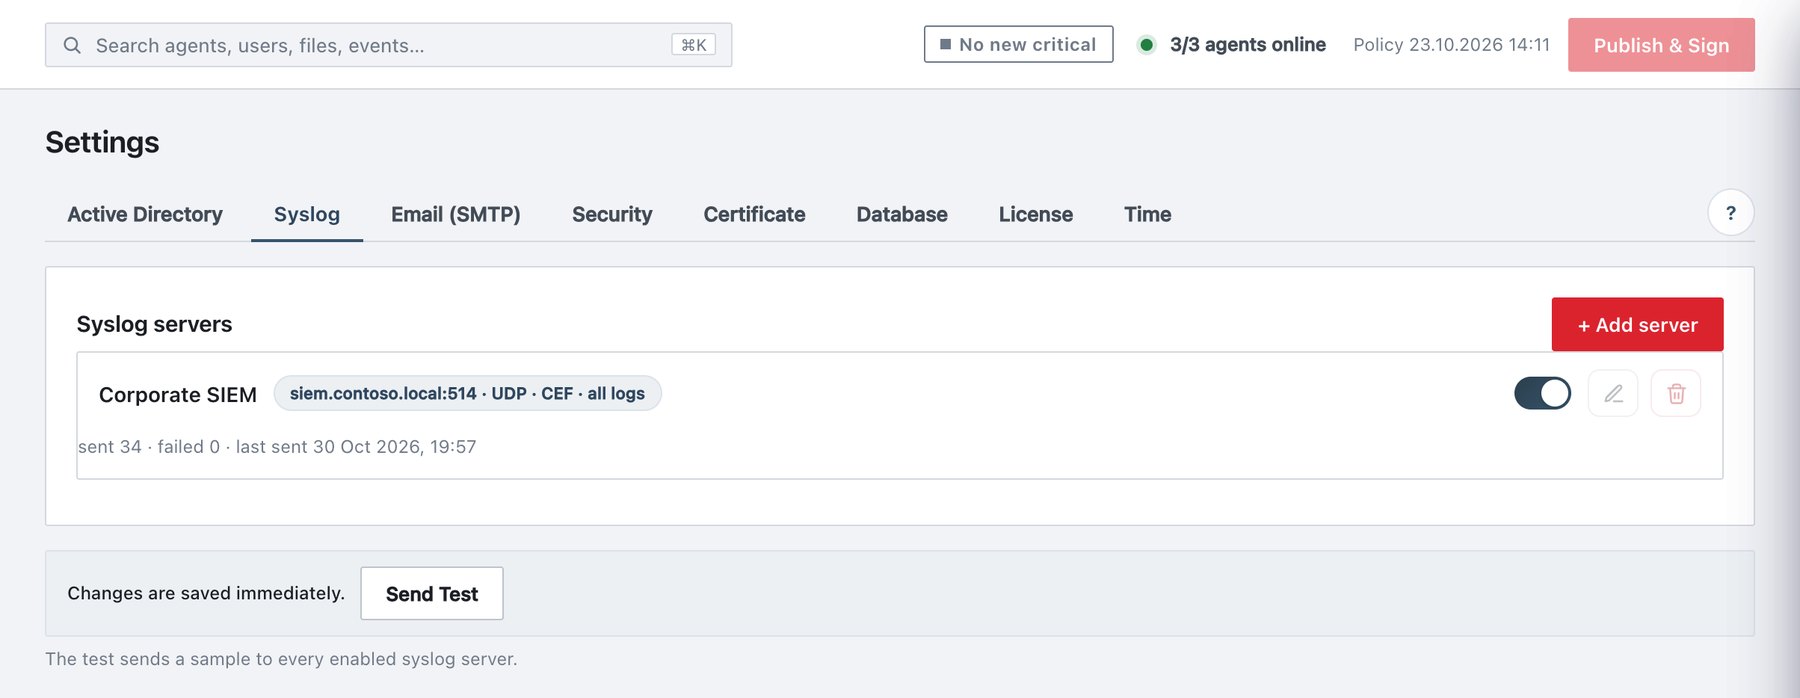
What the page shows
Syslog servers card with + Add server and one row per server:
- Name (or host, or Unnamed server).
- Summary badge:
host:port · UDP|TCP|TCP+TLS · CEF|RFC3164 · all logs | N events. - disabled, no host and N failed badges where applicable.
- An on/off switch (A disabled server receives nothing), Edit, Delete.
- Delivery line (administrators only):
sent N · failed N · last sent … · last error: … (time), counted since the API service last started and refreshed every 30 seconds.
Below the card: Changes are saved immediately., Send Test and the per-server test result.
Add a server
- Click + Add server. The New syslog server panel opens.
- Fill in the fields below.
- Click Test in the panel to send a sample to this server only, before saving.
- Click Save (applies immediately).
- Click Send Test on the page to test every enabled server; the result lists each server as Sent or Failed (Syslog test — N of M servers OK).
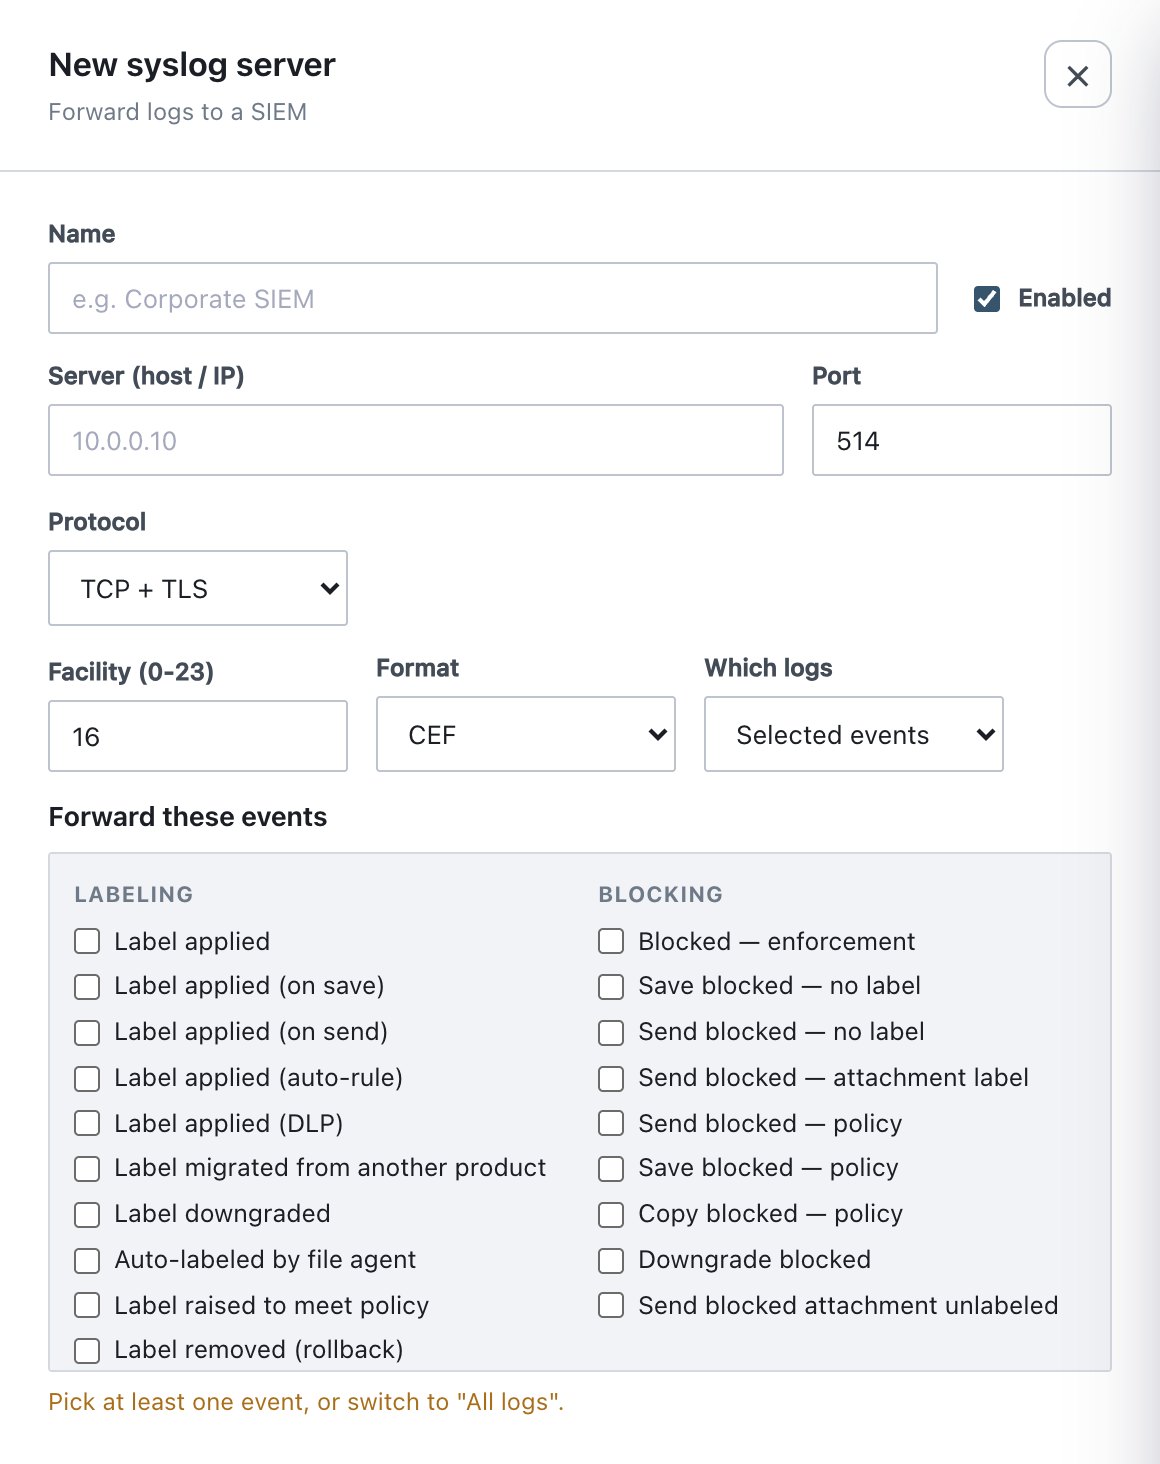
| Field | What it does | Default / allowed values |
|---|---|---|
| Name | Label in the list. | Optional, e.g. Corporate SIEM. |
| Enabled | Disabled servers receive nothing. | On. |
| Server (host / IP) | SIEM collector. | Required (a server without host receives nothing). |
| Port | Collector port. | Default 514; 1–65535. |
| Protocol | Transport. | UDP (default), TCP, TCP + TLS. |
| Facility (0-23) | Syslog facility in the PRI value. | Default 16 (local0). |
| Format | Message format. | CEF (default) or RFC3164 (plain). |
| Which logs | Scope. | All logs (default) or Selected events. |
| Forward these events | Event picker (Selected events only), grouped as Labeling, Blocking, Detection, AI classification, Content warnings, Masking, Printing & screen watermark, Security & tamper, Agent errors, Administration, Agent operations, License, System. | Pick at least one event, or switch to All logs. |
Transport details
| Protocol | Behaviour |
|---|---|
| UDP | Connectionless; no delivery confirmation. Tests and the 15-minute check can only detect “nothing listening” or “host unreachable”. Confirm receipt in the SIEM. |
| TCP | Persistent connection, one message per line (newline framing). Up to 1000 messages are queued per server while disconnected; reconnection backs off up to 60 seconds; connect timeout 4 seconds. |
| TCP + TLS | As TCP, with TLS. The SIEM certificate is always verified. A
private-CA certificate is trusted only if that CA was added at
installation (ADA_EXTRA_CA_CERTS); there is no console
switch to skip the check. |
Message formats
Every message has an RFC 3164 header:
<PRI>Mmm dd hh:mm:ss ada-api <message>, where
PRI = facility × 8 + severity. Control characters in the message are
replaced by spaces (no injected lines).
RFC3164 (plain) body:
[Ada] <name> (user: <user>): <message>.
CEF body:
CEF:0|Ada|Ada Data Classification|1.0|<signature>|<name>|<cef-severity>|rt=<ms> suser=<user> act=<event> msg=<message>
| CEF field | Content |
|---|---|
| Device Vendor / Product / Version | Ada / Ada Data Classification /
1.0 |
| Signature ID | The audit event identifier, e.g. admin_login_failed,
security_config_changed |
| Name | For audit events, the event identifier. For monitoring events a
short title: TLS certificate, Disk space,
Container status change. The test message uses
test_alert / Ada test alert. |
| Severity | Mapped from the syslog severity (table below). |
rt |
Time in milliseconds since 1970 (UTC). |
suser |
The acting user (labelling user, administrator or user name from the
record), system for monitoring events, ? when
unknown. |
act |
The event identifier. |
msg |
For audit events, the event identifier; for monitoring events a readable description. |
\ and | are escaped in the header;
\, = and line breaks in extension values.
Severity mapping
| Syslog severity | CEF | Events |
|---|---|---|
| 2 critical | 10 | audit_chain_broken, license_expired,
tls_cert_expired |
| 3 error | 8 | Licence events, blocked actions, security and tamper events, agent
errors, backup_failed, ai_training_failed;
certificates expiring within 7 days; container errors |
| 4 warning | 6 | agent_offline, container warnings,
tls_cert_expiring (≤ 30 days), disk_low (<
15 % free), ai_type_deleted |
| 5 notice | 5 | tls_cert_ok, disk_ok, test messages |
| 6 informational | 3 | Everything else: labelling, detection, administration,
agent_online, etc. |
All logs covers every audit record plus the monitoring events: container status changes, audit-chain breaks, agents going offline/online, certificate expiry bands and disk space.
Behaviour
- A failed delivery marks syslog DOWN in System at
once; the 15-minute check confirms recovery. Transitions write
service_down/service_restored(service Syslog). - Delivery status also appears in System (health panel and Syslog log) and on Status.
- Changes write
alert_config_changed, naming added, removed and changed servers.